
Block’s Bitcoin Engineering and Security team and independent Bitcoin Core developers have traced the recent batch of Coinkite Coldcard wallet losses to a specific firmware defect that exposed a hidden weakness in Bitcoin self-custody before any user touched a seed phrase.
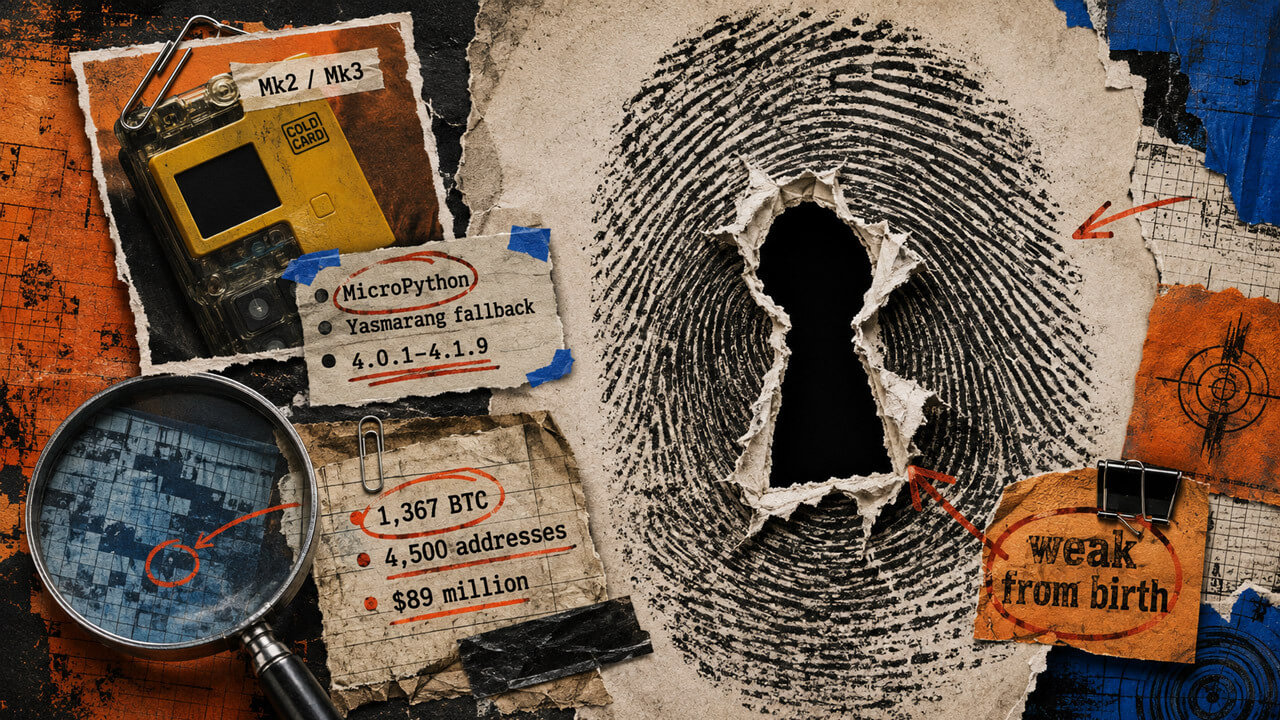
The bug diverted the device’s random-number generation from its STM32 hardware source to MicroPython’s deterministic Yasmarang fallback.
Mk2 and Mk3 devices running firmware 4.0.1 through 4.1.9 produced seeds whose cryptographic randomness collapsed into a small, searchable set.
Mk4, Q, and Mk5 models were less severely affected, producing seeds with about 72 bits of entropy, still well under the 128 bits specified by the design.
How weak seeds compromised Bitcoin self-custody
A user could write down twelve or twenty-four words, store them in a safe, keep the device offline for years, and still hold a key an attacker could reconstruct by searching the fallback generator’s narrow output space.
A firmware fix protects only the seeds a device generates once the owner installs the update, so any seed the flawed path already generated needs full replacement: Coinkite’s advisory directs affected users to generate an entirely new seed and move their funds.
Importing the old phrase into a different manufacturer’s wallet carries the same weakness. The flaw traces to the seed’s origin, a property that travels with the recovery words themselves.
| Layer of custody | What users thought they were securing | What the Coldcard flaw exposed |
|---|---|---|
| Seed generation | Random words created securely by the device | Some seeds were weak from birth |
| Offline storage | Recovery phrase kept away from attackers | Safe storage could not fix weak entropy |
| Firmware update | Device can be patched | Existing weak seeds could not be repaired |
| Device migration | Import phrase into safer hardware | Weakness followed the recovery words |
| User behavior | Avoid phishing, malware, leaks | Loss could happen without user mishandling |
For a portion of affected owners, the instant the device generated a key, months or years before any deposit arrived, fixed the search space regardless of how carefully the owner stored the resulting phrase afterward.
Coldcard built its reputation on the features security guides recommend for Bitcoin self-custody: Bitcoin-only firmware, air-gapped signing, dual secure elements, published source code and reproducible builds.
Rebuilding the published firmware and matching it against the distributed binary confirms the code users run matches the code Coinkite published. That match speaks to distribution integrity alone, and catching a defect in the underlying design requires a separate, deeper audit of the source itself.
The vulnerable path shipped in firmware that Coinkite released starting in 2021 and continued to ship until this July’s disclosure, a five-year window during which the source code was public and the flaw went undetected.
Coinkite’s technical notes say that prior review confirmed that the correct hardware random-number generator existed somewhere in the firmware binary, but stopped short of confirming that the seed-generation routine reached it.
The owners who added a second assumption
Owners who set a strong, unique BIP-39 passphrase resisted the seed-reconstruction attack on its own, because BIP-39 derives the wallet seed from the mnemonic combined with a salt containing the passphrase.
A different passphrase produces a different wallet even when the underlying words match.
That passphrase sits apart from the device PIN, which only unlocks the hardware; the passphrase itself participates in generating the keys, and Coinkite still recommended migration for these users.
Owners who generated their seed with at least 50 fair, independent, private dice rolls form the second group Coinkite excludes from this specific flaw, since adding external entropy removed the device’s defective generator as the sole input.
Andrew Mannoukas, chief information security officer at Xapo Bank, framed the pattern in a note to CryptoSlate:
“The lesson of this incident isn’t that hardware wallets are bad; it’s that concentration is. When the security of your Bitcoin is reduced to a single secret, created on a single device, in a single unrepeatable moment, you’ve inherited every assumption that is baked into that moment.”
He added that the industry data has been telling for years that the majority of losses now come from key management and operational failures.
Casual advice about multisig often leaves out one catch: a 2-of-3 arrangement blocks a single compromised key from moving funds. Three keys that share the same defective implementation collapse into a single failure domain.
Coldcard’s own documentation allows a single device to produce multiple cosigners using different passphrases, creating separate keys that can still trace back to a single underlying implementation.
The real test shifts from whether a wallet uses multisig to who generated each key, which implementation it uses, and with which source of randomness.
| Setup | What it added | Why it mattered in this incident | Remaining caveat |
|---|---|---|---|
| Device-generated seed only | No second assumption | Security depended heavily on Coldcard’s RNG path | Fully exposed if seed was predictable |
| Strong BIP-39 passphrase | Independent secret | Weak mnemonic alone was insufficient | Weak passphrases may still be guessed |
| 50+ private dice rolls | External entropy | Device RNG was not the only randomness source | User must generate rolls correctly |
| Diversified multisig | Independent signing keys | One weak key may not meet spending threshold | Keys must come from independent sources |
| Same-device multisig | More keys, same implementation | May look safer without real independence | Shared failure domain remains |
Ledger’s mirror image
Ledger’s optional Recover service causes the device’s Secure Element to duplicate and encrypt the wallet’s entropy, split the result into three encrypted fragments, and send them to separate backup providers, a process that requires both a subscription and physical approval on the device itself.
Ledger’s version of the boundary problem involves moving secret material outside the device, under defined conditions the user approves each time.
Coinkite’s problem sat further upstream: the firmware undermined the secret before the device’s boundary ever came into play. In both cases, the manufacturer’s software determines where the true security boundary of Bitcoin self-custody lies, regardless of the marketing language used for the hardware.
Initial sweeps pulled roughly 594 BTC from about 500 wallets. On-chain researchers have since linked at least three suspected waves to the flaw, totaling nearly 1,367 BTC across more than 4,500 addresses, worth roughly $89 million at the time.
Reports circulating Aug. 3 describe a possible fourth wave that could push the total toward $114 million. Galaxy Digital’s Alex Thorn cautioned that blockchain patterns alone do not confirm the link between some swept addresses and vulnerable Coldcard firmware, leaving attribution provisional as the total continues to climb.
A subsequent Aug. 4 update from Lookonchain, citing Galaxy Research, estimated that Coldcard-related losses may have reached 2,055 BTC, worth roughly $130 million, across more than 7,700 affected addresses.
TRM Labs found that infrastructure and operational compromise, chiefly private-key and seed-phrase theft, accounted for about 76% of the value stolen in crypto hacks during the first half of 2026. Those same failures made up roughly 15% of total incidents.
CertiK separately counted wallet compromise as the costliest attack category over the same period, at more than $444 million across 33 incidents. Attackers have found more profit chasing the systems and processes around keys than chasing the cryptography underneath them.
Coinkite founder Rodolfo Novak apologized publicly, said the company takes full accountability, and offered help with police reports, insurance claims and blockchain investigations. As of Aug. 3, reimbursement was not among the listed fixes.
An exchange that loses customer funds can sometimes draw on reserves, insurance or a balance sheet a company built for that purpose. A hardware wallet maker sells a product and typically leaves custody of the underlying Bitcoin with the user alone, leaving responsibility for any defect unresolved between the user and the manufacturer.
What happens next for Bitcoin self-custody
All things being well, migration outpaces the emergence of any new wave, and wallet makers respond with entropy attestations, seed-generation testing, and clearer tooling for emergency key rotation.
Passphrases, external dice entropy, and properly diversified multisig graduate from advanced tips to default guidance, and the industry treats the episode as the moment when self-custody standards caught up with self-custody marketing.
However, in the future, researchers could uncover additional weak-seed paths in other models or setup routines, and confidence could erode faster than manufacturers can patch them.
Panicked migrations create their own losses, through address-reuse mistakes, rushed transfers, and a fresh wave of wallet-support scams that target the users trying to move funds to safety.
| Scenario | Trigger | Likely market response | What it means for Bitcoin self-custody |
|---|---|---|---|
| Bull case | Losses stabilize and migrations work | Wallet makers add entropy tests, attestations, and clearer emergency rotation tools | Self-custody matures from seed possession to layered failure resistance |
| Bear case | More weak-seed paths appear | Users panic-migrate, scammers exploit confusion, trust in hardware wallets falls | “Not your keys” gets replaced by “who created your keys?” |
| Industry adaptation | Standards emerge around entropy, audits, and multisig diversity | Advanced practices become default wallet UX | Self-custody becomes more resilient but less simple |
| Accountability gap persists | No clear reimbursement or liability norm forms | Users keep control but bear more product-defect risk | Hardware-wallet trust becomes part of custody risk analysis |
Holding your own keys strips an exchange of its power to freeze a withdrawal, rehypothecate a balance, or collapse into insolvency with customer funds inside it.
One dependency survives inside Bitcoin self-custody: the manufacturer standing behind the device that turns randomness into a key.
A single seed, born on one company’s hardware in one unrepeatable moment, functions as sovereignty only once a second, independent assumption stands behind it.
Featured,Hacks,Wallets#Coldcard #flaw #exposes #hidden #risk1785837546
