What's Hot

    Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

    October 5, 2026

    Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

    October 5, 2026

    NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

    October 5, 2026
    Facebook Twitter Instagram
    • Business
    • Markets
    • Get In Touch
    • Our Authors
    Facebook Twitter Instagram
    Crypto News: Latest Cryptocurrency News and Analysis
    • Home
    • Business

      Fidelity Buys 7.4% Of Bitcoin Mining Company Marathon Digital Holdings

      February 11, 2021

      Twitter Reacts as Auto Driver Begins Accepting Crypto as Payment

      February 11, 2021

      HSBC Becomes Latest Bank to Suspend Payments to Crypto

      February 4, 2021

      Bitcoin Holds Support; Approaching $50K Resistance

      February 4, 2021

      Cryptocurrency Prices Today: Bitcoin Up Over $47,000, Ether Rises 3%

      February 3, 2021
    • Technology
      1. Business
      2. Insights
      3. View All

      Fidelity Buys 7.4% Of Bitcoin Mining Company Marathon Digital Holdings

      February 11, 2021

      Twitter Reacts as Auto Driver Begins Accepting Crypto as Payment

      February 11, 2021

      HSBC Becomes Latest Bank to Suspend Payments to Crypto

      February 4, 2021

      Bitcoin Holds Support; Approaching $50K Resistance

      February 4, 2021

      Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

      October 5, 2026

      Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

      October 5, 2026

      NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

      October 5, 2026

      Coinbase says AI support tests fell from weeks to minutes

      October 5, 2026

      Bitcoin Climbs as Elon Musk Says Tesla ‘Likely’ to Accept it Again

      March 16, 2021

      Can Cryptocurrency Be Hacked, Stolen Or Scammed? How Can You Be Safe?

      February 11, 2021

      How Investors Can Get In On Crypto Without Actually Buying Any

      February 4, 2021

      Ethereum Just Underwent a Major Change – Hence, The 25% Jump in a Week!

      February 4, 2021
    • Insights
      1. Bitcoin
      2. Ethereum
      3. Eurozone
      4. Monero
      5. View All

      Bitcoin Tops $86K Amid Strong ETF Inflows, 3x Crypto Products Win Approval

      October 5, 2026

      OpenAI Agent Incidents Spread Across Australian Government Sites as Review Costs Soar

      October 5, 2026

      China’s Spies Put Crypto Under the Microscope

      October 5, 2026

      Trump Launches ‘Super Intelligence Force’ to Drive US AI Leadership

      October 5, 2026

      Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

      October 5, 2026

      Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

      October 5, 2026

      NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

      October 5, 2026

      Coinbase says AI support tests fell from weeks to minutes

      October 5, 2026

      PI dips below $0.090 as bearish momentum builds despite rising OI

      October 5, 2026

      Dogecoin tops $0.096 as ETF inflows and derivatives signal improving sentiment

      October 5, 2026

      Vaults, Protocol Yield, Staking, and Grid Bots

      September 30, 2026

      What to Test Before You Pay

      September 30, 2026

      CAC Grading Auction Generates Six Figures for Numismatic Groups

      October 3, 2026

      U.S. Mint Launches Supergirl Gold Coin & Medals With Krypto

      October 1, 2026

      Saint-Gaudens Coin and Medal Set Debuts at No. 1

      September 30, 2026

      403-Mintage Team USA Privy Silver Eagle Heads to Auction

      September 29, 2026

      Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

      October 5, 2026

      Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

      October 5, 2026

      NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

      October 5, 2026

      Coinbase says AI support tests fell from weeks to minutes

      October 5, 2026
    • Markets
    • Get In Touch
    Crypto News: Latest Cryptocurrency News and Analysis
    Home » Attackers drove 63% of early use of Ethereum’s new smart wallet feature
    Ethereum

    Attackers drove 63% of early use of Ethereum’s new smart wallet feature

    行政By 行政August 21, 2026No Comments6 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ethereum’s shortcut to smart wallet behavior arrived with a new trust problem: a wallet can make a regular address programmable without moving the user’s assets, while the delegated code gains power to act with that account’s authority.

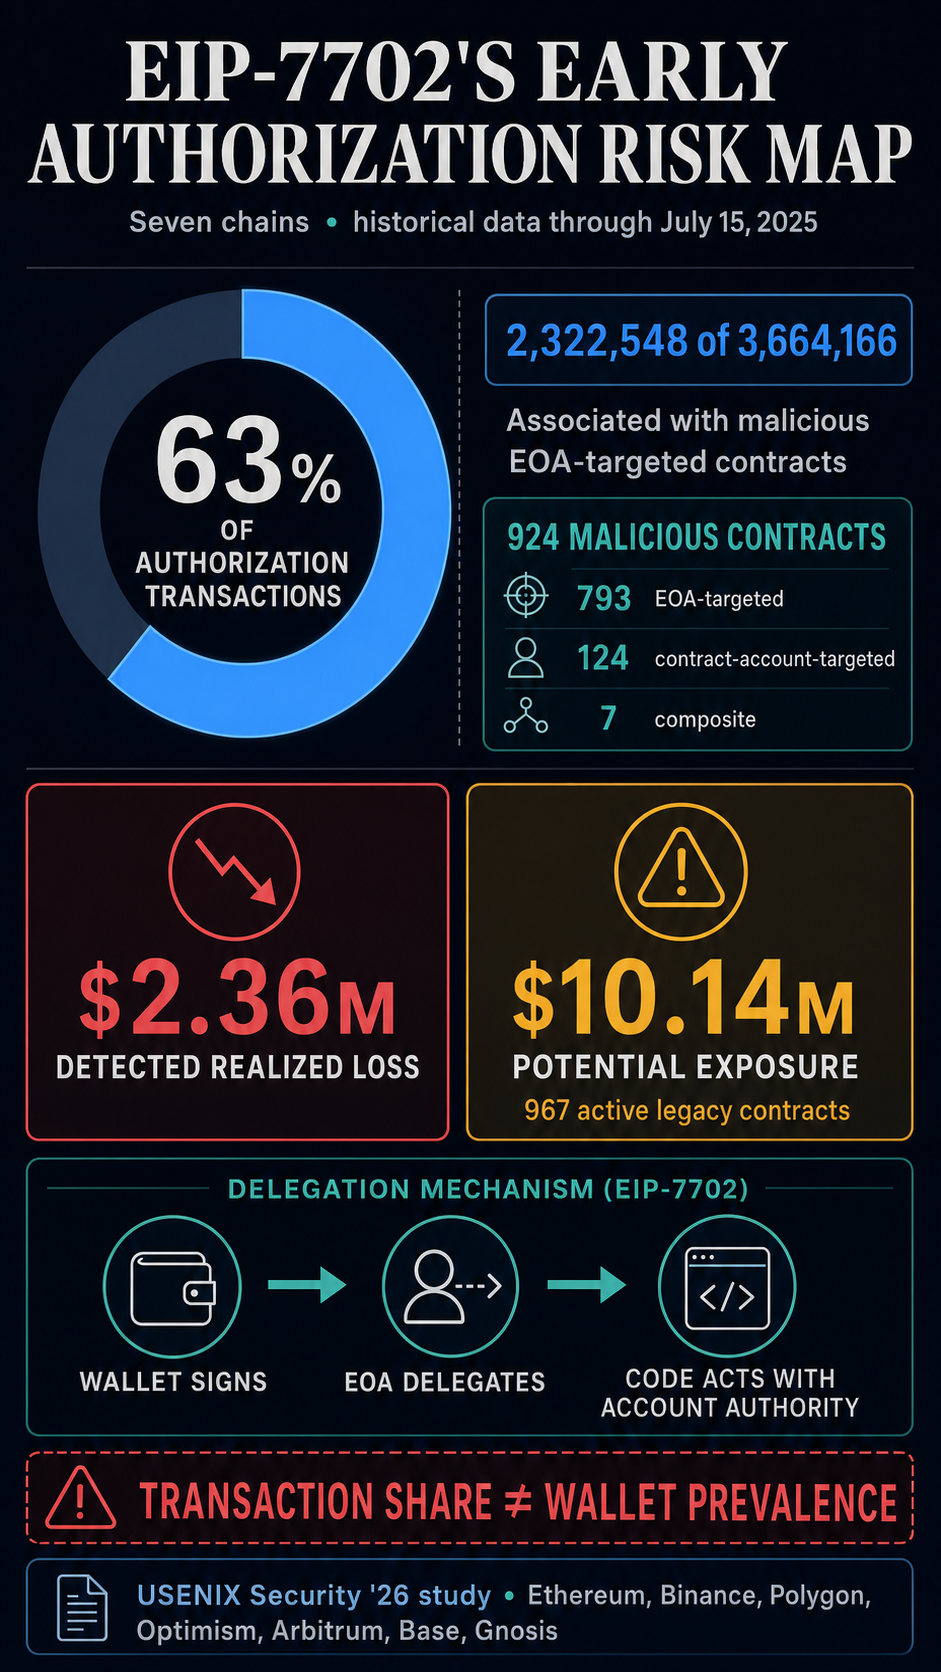
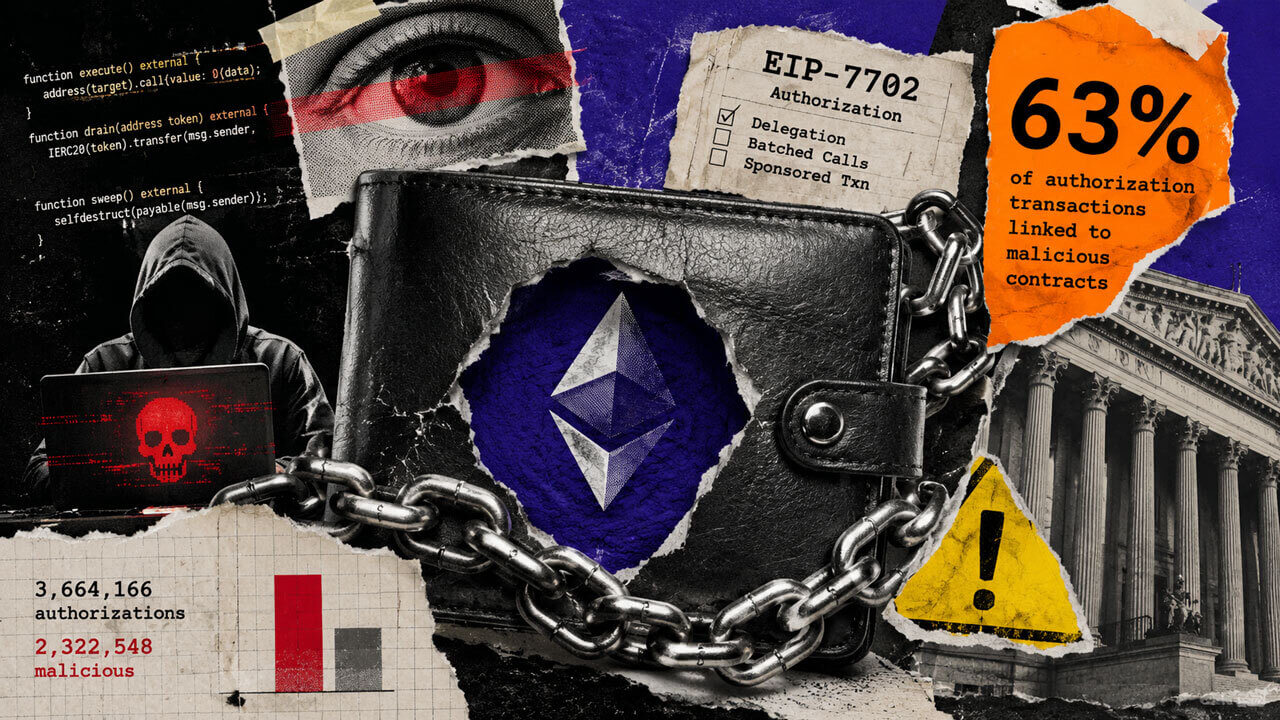
    A peer-reviewed study released for USENIX Security ’26 found that attacker-linked contracts were associated with 2,322,548 of the 3,664,166 EIP-7702 authorization transactions it observed across seven chains through July 15, 2025. That is 63% of the historical transaction volume in the researchers’ dataset.

    The authors tied a relatively small set of malicious contracts to repeated authorizations and described some attacker-controlled activity as likely practice or proof-of-concept testing during an early, exploratory phase.

    The figure measures transactions, while distinct-wallet prevalence and the current 2026 attack rate sit outside the study’s scope.

    Why attackers dominated the early authorization count

    Ethereum activated Pectra, including EIP-7702, on May 7, 2025. The final specification introduced a type-4 transaction that lets an externally owned account set a pointer to deployed contract code.

    The address stays the same, the original private key retains control, and calls to the account can execute the delegated code in the account’s context.

    That design can give a conventional wallet features associated with smart accounts, including batched calls and sponsored transactions, without forcing the user to migrate to a new address. It also turns the delegation target into wallet infrastructure.

    Buggy or hostile code may be able to make approvals, transfers and application calls as the account.

    It says applications should not expect to ask users for arbitrary authorization signatures because there is no safe generic interface for users to assess code with unrestricted account access. Wallets are expected to vet the implementation.

    Attackers could prepare authorization fields off-chain and ask a victim to sign, and a wallet might reduce the decision to a high-level account-upgrade prompt while obscuring the contract address or code receiving authority.

    The protocol verifies the account owner’s signature, while the wallet still has to establish whether the selected code deserves control.

    Related Reading

    Crypto investor loses $1M in Uniswap scam exploiting Ethereum’s EIP-7702

    The researchers analyzed more than 22.8 billion historical transactions on Ethereum, Binance Smart Chain, Polygon, Optimism, Arbitrum, Base, and Gnosis.

    Within that data, they examined 3,664,166 EIP-7702 authorizations through the cutoff and used transaction filters, bytecode analysis and manual review to identify 924 malicious contracts. They classified 793 as EOA-targeted, 124 as contract-account-targeted and seven as composite attacks.

    Study measure What it captures
    3,664,166 authorizations Historical EIP-7702 transactions across seven chains through July 15, 2025
    2,322,548 authorizations, or 63% Historical transactions associated with malicious EOA-targeted contracts
    924 malicious contracts The detected and manually reviewed set under the researchers’ method
    $2.36 million Detected realized loss across three attack categories
    About $10.14 million Potential exposure in a separate legacy-contract subset
    Infographic showing 63% of 3,664,166 historical EIP-7702 authorization transactions associated with malicious EOA-targeted contracts, 924 malicious contracts, $2.36 million in detected realized loss, and $10.14 million in potential exposure.Infographic showing 63% of 3,664,166 historical EIP-7702 authorization transactions associated with malicious EOA-targeted contracts, 924 malicious contracts, $2.36 million in detected realized loss, and $10.14 million in potential exposure.
    An EIP-7702 risk map shows 63% of authorizations, $2.36 million in detected losses, and $10.14 million in potential exposure.

    The paper says malicious contracts were reused disproportionately, so transaction counts can rise much faster than the number of distinct contracts or affected users. In a young authorization market, that repeated attacker activity had an outsized effect on the denominator.

    The Daily Brief

    The signal, before the noise.

    Start your day with the crypto stories moving markets, decoded by CryptoSlate’s editors.

    One email. Everything that matters.

    Free to join. Unsubscribe any time.

    Whoops, looks like there was a problem. Please try again.

    You’re on the list. Your next Daily Brief is on its way.

    Attackers found a repeatable route to account-level authority before wallets had made the trust decision as legible and constrained as the power it conveyed.

    The risk reaches beyond hijacked wallets

    The study measured $2,362,848.76 in realized losses across its three attack categories. A separate estimate covered older contracts whose defenses assumed that programmable EOAs could not exist.

    EIP-7702 breaks the old assumption that msg.sender == tx.origin reliably identifies a plain EOA or blocks contract-mediated behavior.

    The researchers identified 967 active Ethereum contracts in a subset using that check as a flash-loan defense and estimated that about $10.1 million in assets were at potential high risk.

    Detected theft totaled about $2.36 million, so the $10.14 million represents assets exposed by a defensive assumption that no longer held.

    The researchers observed attackers rebinding accounts to benign code after an attack, making current-state-only monitoring unreliable. They also found 500 special nonzero delegation targets with no deployed code.

    A precomputed CREATE2 address could receive code later, changing what the account executes while the recorded target stays the same.

    Those patterns make authorization history part of the security boundary. Wallets and monitoring tools need to remember where an account previously pointed, evaluate changes in delegated code, and treat an undeployed target as unresolved rather than harmless.

    The authors’ rules may miss malicious contracts before preparation transactions become visible or attacks using novel interfaces outside the method’s coverage. The 924 contracts are the detected and manually verified set, while the total universe of abuse remains unknown.

    Safe default behavior starts with making delegation a wallet-controlled installation decision. Post-study ethereum.org guidance calls for whitelisting delegation contracts, prominently displaying the target, avoiding arbitrary delegation on hardware wallets, and relying on audited implementations.

    An account-abstraction wallet capability proposal takes the same direction, calling for a strict shortlist of well-known, publicly audited smart account implementations. These documents do not measure how consistently production wallets have adopted it.

    Applications should request the feature they need and leave the account implementation to the wallet. For an approval and swap in one flow, current Ethereum Foundation guidance points developers to a wallet interface such as ERC-5792.

    The wallet can then choose EIP-7702, ERC-4337, or another account system without asking the user to approve low-level delegation code selected by the application.

    Current guidance recommends signing initialization parameters or restricting setup to the ERC-4337 EntryPoint, closing a front-running path in which an attacker substitutes their own values.

    The study identified a related failure mode in legacy wallet code: constructors do not run again when an account delegates to an existing contract, which can leave ownership unset and externally claimable.

    A benign current pointer cannot erase a malicious history, and a target with no code may acquire behavior later. Wallets need durable authorization records, clear alerts when the delegation changes, and a removal path that users can understand.

    Making the EIP-7702 wallet programmability safe by default requires wallets to treat delegation as installation of the account’s control plane: restrict who can request it, expose exactly what will control the account, verify how it initializes, and keep watching after the pointer changes.

    Featured,Hacks,Technology,Wallets,ethereumethereum#Attackers #drove #early #Ethereums #smart #wallet #feature1787297954

    attackers drove Early Ethereum Ethereums Feature smart wallet
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    行政
    • Website

    Related Posts

    Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

    October 5, 2026

    Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

    October 5, 2026

    NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

    October 5, 2026

    Coinbase says AI support tests fell from weeks to minutes

    October 5, 2026
    Add A Comment

    Leave A Reply Cancel Reply

    Top Posts

    Millennials Are Quitting Job to Become Day Traders

    January 20, 2021

    Jack Dorsey Says Bitcoin Will Unite The World

    January 15, 2021

    Hong Kong Customs Arrest Four in Crypto Laundering Bust

    January 15, 2021

    Subscribe to Updates

    Get the latest sports news from SportsSite about soccer, football and tennis.

    Advertisement
    Demo

    Your source for the serious news. This demo is crafted specifically to exhibit the use of the theme as a news site. Visit our main page for more demos.

    We're social. Connect with us:

    Facebook Twitter Instagram Pinterest YouTube
    Top Insights

    Strategy buys just 334 Bitcoin as preferred-share buybacks reach $1.45 billion

    October 5, 2026

    Metaplanet sold 10,000 Bitcoin in a credit-rating bid, only to buy back 11,000 BTC at a higher price per coin

    October 5, 2026

    NYSE owner and OKX plan 24/7 tokenized stock trading using Uniswap

    October 5, 2026
    Get Informed

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook Twitter Instagram Pinterest
    • Home
    • Business
    • Markets
    • Technology
    • Contact us
    © 2026 ThemeSphere. Designed by WPfastworld.
    • Easterngifts
    • koreanbj
    • korean bj porn​
    • korean bj nude

    Type above and press Enter to search. Press Esc to cancel.